How can a transaction that appears to be a routine token swap expose a user to several independent risks at once? The answer lies in a basic but often overlooked fact: DeFi users do not transact with “the app” in a general sense. They authorize specific instructions sent to smart contracts, often across unfamiliar chains, with consequences that may be difficult to reverse. The wallet is therefore more than a key holder. It is the interface where code, incentives, permissions, and human judgment meet.
This matters especially for US users moving between Ethereum and other EVM-compatible networks. A familiar interface can conceal different fee markets, bridge assumptions, contract deployments, and asset representations. A multi-chain wallet may make this movement more convenient, but convenience does not remove the need to inspect what a transaction will do. The central question is not whether a wallet can sign quickly. It is whether it can help a user understand the transaction before signing.
From address book to transaction interpreter
Early cryptocurrency wallets were primarily built around sending and receiving native assets. The user selected an address, entered an amount, and signed a relatively direct transfer. DeFi changed the task. A swap, lending deposit, liquidity position, or staking action usually involves a smart contract: a program deployed on a blockchain that executes predetermined logic when called.
The visible action may be “swap token A for token B,” but the underlying transaction can include a contract address, a function call, token approvals, slippage settings, routing instructions, and a gas payment. An approval is particularly important. It can grant a contract permission to move a specified amount of a token from the user’s wallet. That permission may remain active after the original trade, depending on the token and the allowance selected.
This creates a useful conceptual distinction: signing is not the same as understanding. A cryptographic signature proves authorization, but it does not guarantee that the user interpreted the request correctly or that the destination contract behaves as expected. Wallet security features are valuable because they can translate technical transaction data into a more legible risk picture before the irreversible step.
The case of a cross-chain DeFi user
Consider a user who holds assets on Ethereum and wants to move capital to an EVM-compatible network to access a lending market. The process may involve selecting a bridge, approving a token, initiating a transfer, waiting for settlement, and then supplying the received asset to a lending protocol. None of these steps is necessarily fraudulent or unusual. Yet each introduces a separate point at which the user must verify the chain, contract, asset, and expected outcome.
Cross-chain activity is often described as if it were simply a wider version of ordinary DeFi. Mechanically, it is more complicated. The receiving asset may be a representation issued through a bridge rather than the original asset native to the source chain. Finality assumptions may differ. A successful transaction on one network does not by itself prove that the intended state has been reached on another. The user is relying on an additional coordination system, with its own validators, messaging design, liquidity, and failure modes.
A multi-chain wallet can reduce operational friction by presenting networks and accounts in one environment. That is useful, but it also creates a boundary condition: a unified interface can make materially different systems feel deceptively similar. The wallet may help identify the chain and display transaction effects, yet it cannot eliminate risks created by a compromised bridge, an illiquid market, a malicious contract, or an economic attack on a protocol.
For this reason, transaction simulation is best understood as a decision aid rather than a guarantee. A simulation estimates the state changes that would result if the transaction were executed under the observed conditions. It can reveal that a user will receive fewer tokens than expected, transfer an unexpected asset, or grant a broad allowance. It may also expose a mismatch between the user’s intention and the call data being signed.
Why simulation improves judgment, but cannot predict everything
Simulation addresses one of the most common DeFi errors: confusing the interface’s label with the transaction’s actual effect. If a user believes they are depositing one asset but the call would transfer another, a clear simulation can interrupt the mistake. If a contract interaction would leave the wallet with an unfamiliar token or a sharply reduced balance, that information is materially more useful than a generic warning icon.
However, the method has limits. Blockchain state can change between simulation and execution. Prices may move, liquidity may be consumed, a transaction may be reordered, or a protocol may depend on external data that changes after the simulation. Some contract behavior is difficult to model completely, particularly where transactions depend on timing, oracle updates, callback logic, or interactions with other pending transactions.
That limitation leads to a sharper rule for advanced users: treat simulation as evidence about a transaction, not as proof of safety. The confidence it provides depends on the quality of the simulated state, the contract’s transparency, the protocol’s assumptions, and the time between inspection and signing. A simulation can answer “what appears likely to happen under these conditions?” It cannot answer every version of “what could go wrong?”
The same distinction applies to security alerts. A warning may identify a suspicious approval, an unknown contract, or a potentially harmful transfer. The absence of a warning is not a certification that the protocol is sound. Security systems are generally better at detecting known patterns and visible inconsistencies than at resolving questions of governance quality, economic sustainability, or newly deployed code.
What changed in the current multi-chain environment
The historical development of DeFi explains why wallet design has become more demanding. First came basic asset custody and transfers. Then decentralized exchanges introduced contract-based swaps. Lending markets, automated market makers, liquid staking, derivatives, and bridges added increasingly complex combinations of permissions and state changes. Each innovation expanded what a wallet could help users do, but also expanded what a misleading prompt or compromised contract could cause.
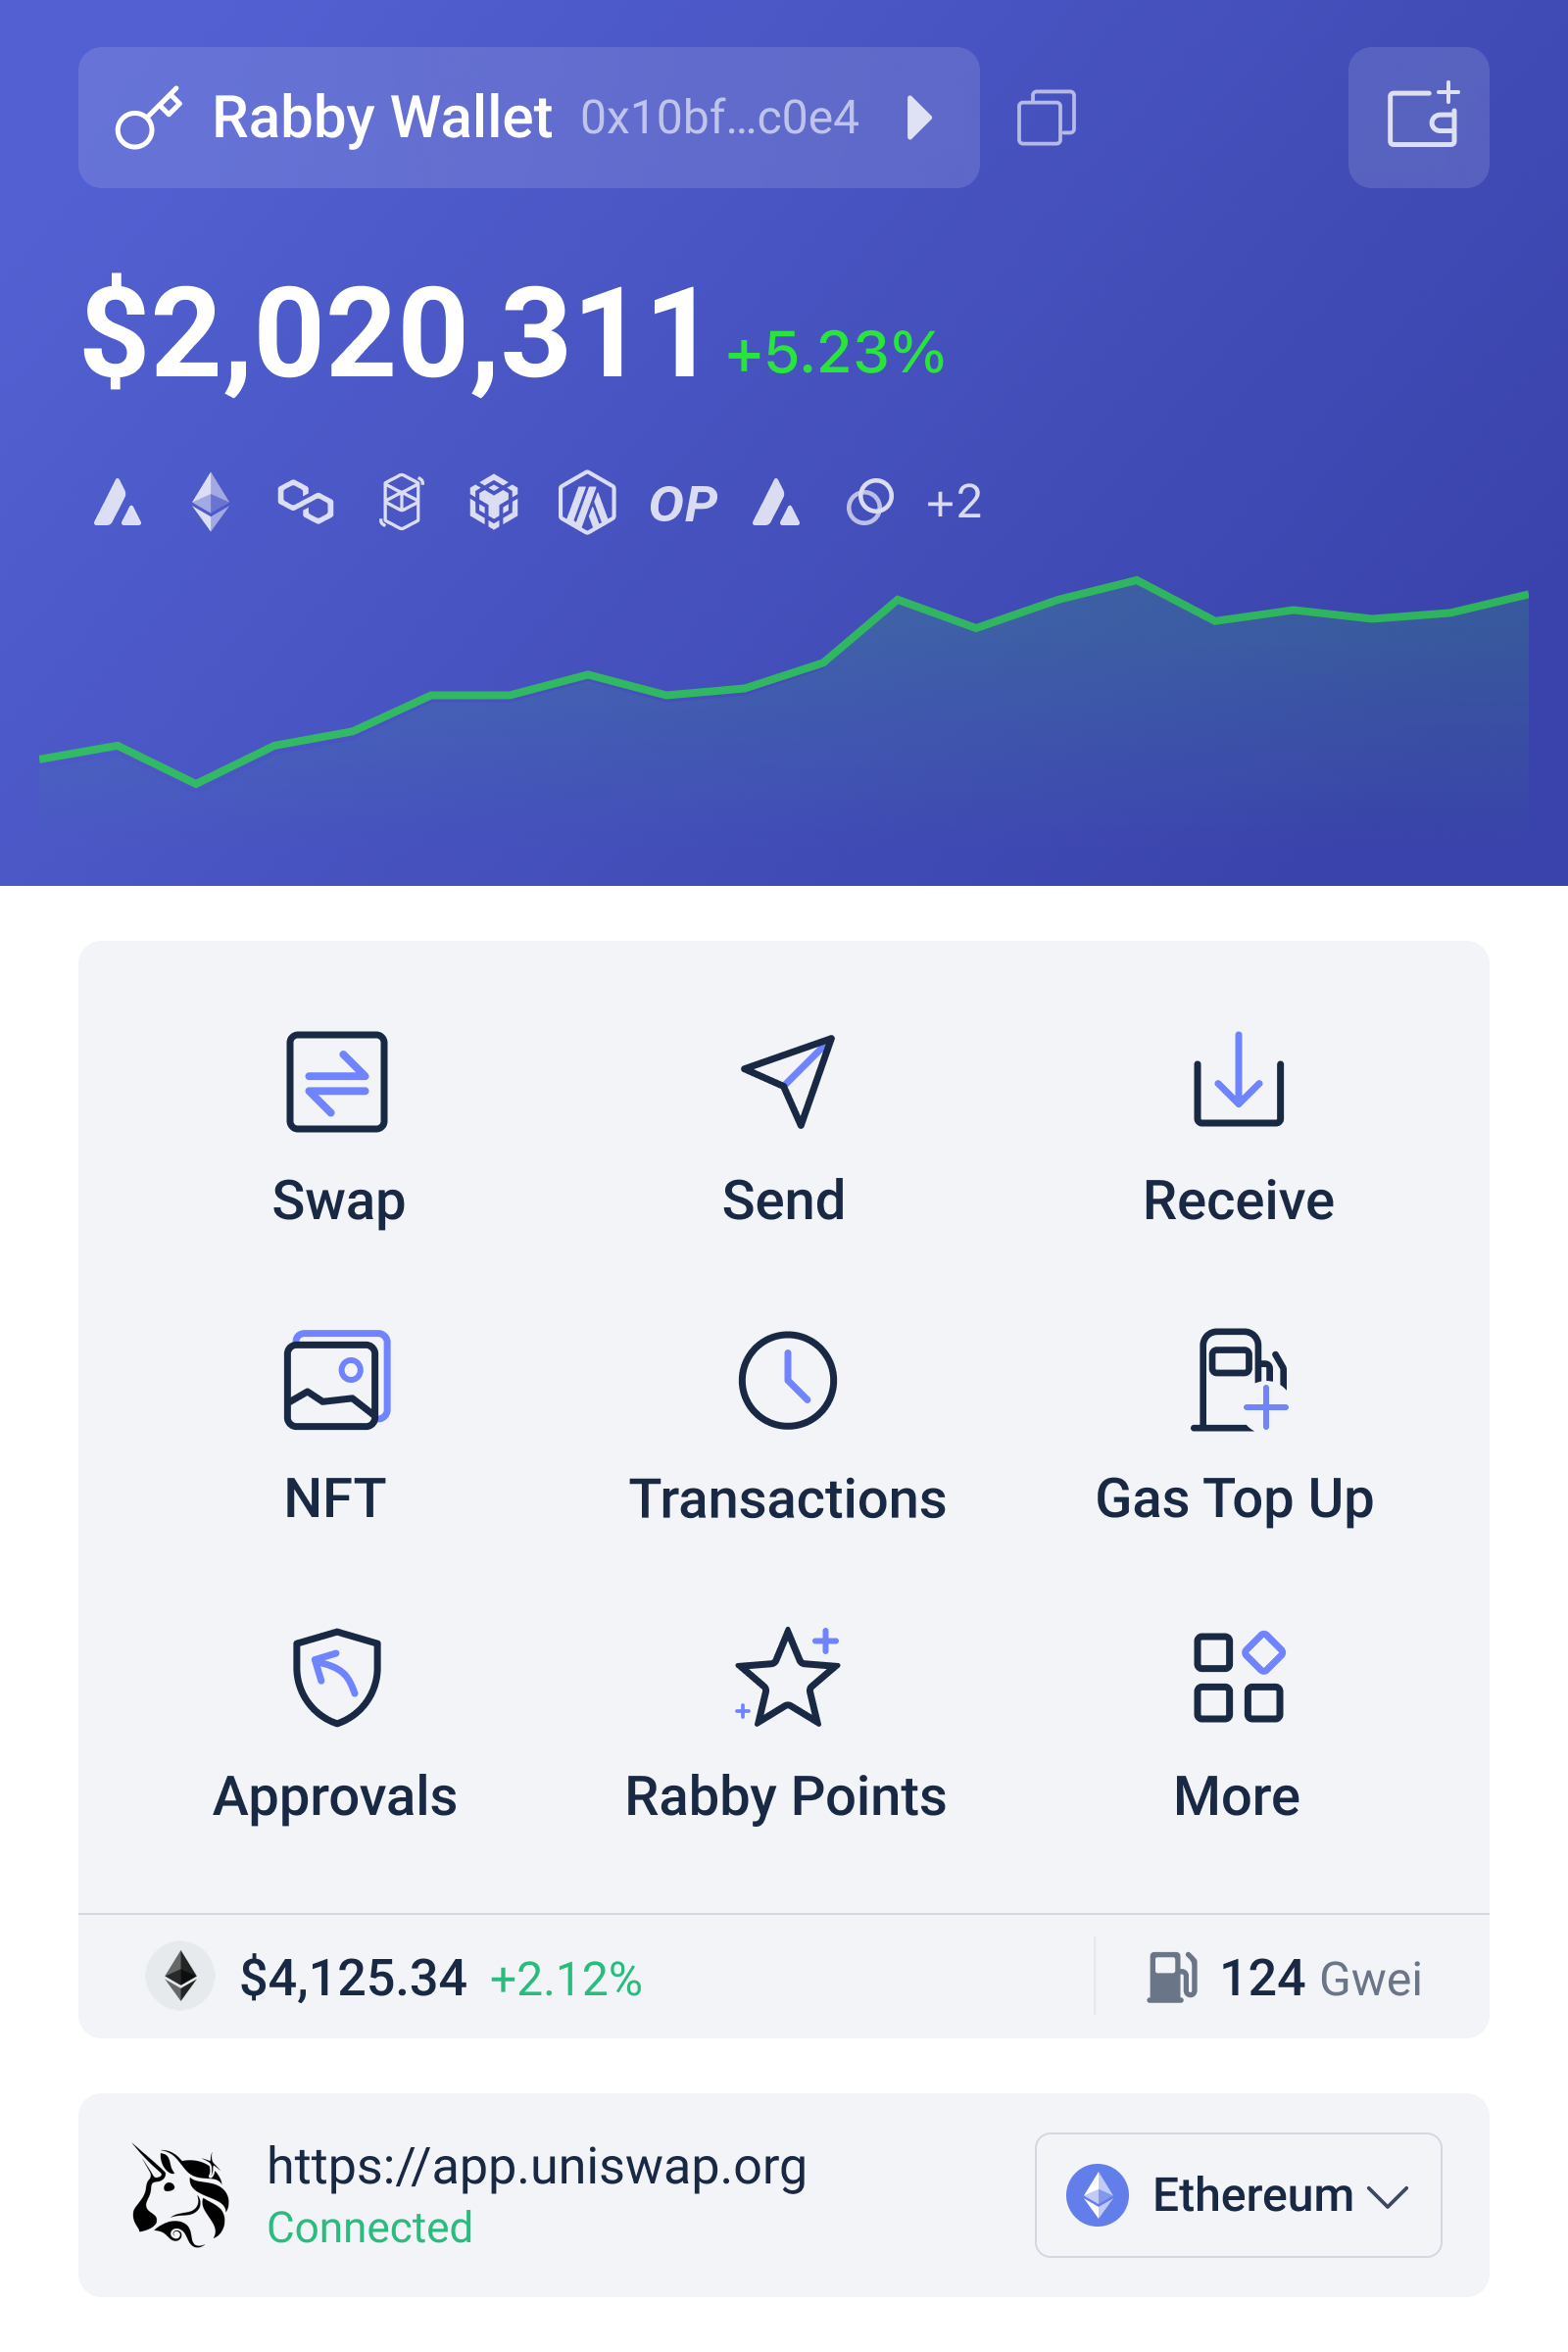
Recent messaging around Rabby Wallet presents it as a wallet for Ethereum and EVM networks, with an emphasis on broad chain coverage, on-chain activity, and use through Chrome and Brave. The practical significance is less about the label “multi-chain” than about the workflow it supports: one user may need to compare transaction behavior across networks without losing visibility into which chain is active and which contract is receiving authority.
For users evaluating a rabby wallet or any comparable tool, the relevant test is not simply how many chains are supported. A more useful evaluation asks whether the wallet makes four things clear before signing: the network, the recipient or contract, the assets leaving the account, and the permissions that remain afterward. These are the control points where convenience should be balanced against verification.
A practical framework for signing DeFi transactions
A reusable review process can be organized around three questions. First, what is the transaction intended to change? This includes the wallet balance, token ownership, debt position, collateral, or liquidity position. Second, what authority is being granted? An approval may be temporary, limited, or effectively broad. Third, what assumptions must remain true for the result to be acceptable? These may include a minimum output, a functioning bridge, a reliable oracle, or a particular chain being selected.
The framework is deliberately broader than checking whether the website looks familiar. Phishing sites can imitate interfaces, and legitimate protocols can still expose users to smart contract bugs, market manipulation, or poorly understood incentives. Conversely, an unfamiliar contract is not automatically malicious. The right response is investigation: verify the domain through an independent channel, inspect the contract and token details, review the proposed state changes, and use a smaller test transaction when the cost is reasonable.
There is also a behavioral trade-off. More warnings and more technical detail can improve safety, but excessive alerts may train users to click through prompts without reading them. Effective wallet design therefore has to prioritize high-consequence anomalies rather than simply displaying more information. The goal is not to turn every user into a smart contract auditor. It is to surface the facts most likely to change a rational signing decision.
For US users, operational discipline also includes tax and record-keeping awareness. Swaps, liquidity activity, staking, and cross-chain transfers can create reporting questions that depend on facts outside the wallet interface. A wallet can improve transaction visibility, but it is not a substitute for professional tax advice or a complete accounting system. This is another boundary between technical security and financial compliance.
What to watch as wallets become more interpretive
The next stage of wallet development is likely to depend on how well interfaces explain intent rather than merely display raw call data. If wallets can reliably show proposed balance changes, approval scope, chain context, and meaningful anomalies, users may make fewer avoidable signing errors. That outcome is conditional, however. It depends on simulation quality, timely chain data, accurate contract labeling, and users retaining responsibility for decisions that no interface can fully automate.
One unresolved issue is how much trust users should place in wallet-provided interpretations. A helpful explanation is itself a layer of software that can be wrong, incomplete, or dependent on third-party data. The long-term challenge is therefore not to replace verification with automation, but to make verification more intelligible. Better interfaces should reduce cognitive load without hiding uncertainty.
The practical lesson is straightforward: a multi-chain wallet is most valuable when it turns a fast signature into an informed decision. Users should still verify the network, inspect the contract action, understand approvals, and recognize that simulated outcomes are conditional. DeFi rewards users who understand mechanisms, not merely interfaces. The wallet can make that understanding easier to apply, but it cannot outsource judgment entirely.
Frequently asked questions
Does transaction simulation make a DeFi transaction safe?
No. Simulation can reveal likely balance changes, approvals, and unexpected contract effects, but it depends on the blockchain state and cannot guarantee that a contract is honest, bug-free, or economically sound. Treat it as an important review layer, not a complete security certificate.
Why are token approvals important?
An approval gives a smart contract permission to move a token from your wallet, often so it can complete a swap or deposit. The amount and duration of that permission matter. A broad or unnecessary approval can increase exposure if the contract is compromised or behaves unexpectedly.
What should I check before using a DeFi protocol on another chain?
Confirm the active network, the official protocol domain, the destination contract, the asset representation, the expected balance changes, and any bridge assumptions. Also review fees, slippage, and approvals. A successful transaction does not automatically mean that the intended cross-chain outcome has been achieved.